
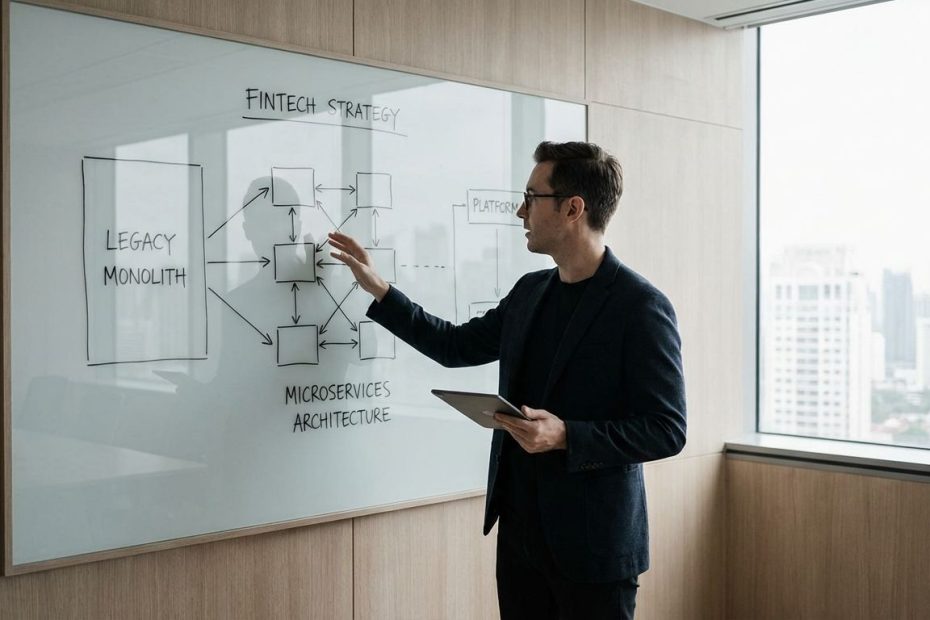
You should move from a monolith to microservices only when the change removes clear delivery, scale, resilience, or compliance bottlenecks. In fintech, the winning move is usually staged modernization, not a dramatic rewrite.
If you are leading a legacy transformation, you need a plan that protects uptime, controls risk, and improves delivery speed without creating service sprawl. This guide shows you where microservices help, where they hurt, how to modernize a fintech stack safely, and what your first year should actually look like when the goal is measurable progress rather than architectural theater.
Should A Fintech Company Really Move From A Monolith To Microservices?
You should not treat microservices as an automatic upgrade. A monolith can still be the right operating model when your product domains are tightly connected, your engineering team is still small, or your release process does not yet require independent deployment across multiple business capabilities. In many fintech firms, the real problem is not the monolith itself. The problem is poor modularity inside it, slow testing, brittle release management, and too much hidden coupling between teams.
A well-structured monolith can serve a company for years if it supports fast releases, clear ownership, and stable operations. That point matters because many modernization programs start with a technology decision when they should start with an operating decision. If your payments flow, onboarding stack, fraud controls, servicing portal, and partner integrations can still move in a coordinated release train without painful delays, you may not need broad service decomposition yet. You may need stronger module boundaries, cleaner interfaces, better build pipelines, and tighter control over change impact.
Microservices begin to make financial sense when business units need different release cadences and different reliability controls. Your lending workflows may need one pace, your customer messaging engine another, and your fraud decisioning pipeline a third. If one minor change forces a full regression cycle across unrelated domains, the architecture is now slowing down the business. That is when service extraction starts to earn its keep.
You also need to weigh the cost of operating a distributed system. Every new service adds deployment pipelines, monitoring, alerting, ownership rules, versioning concerns, network dependencies, security controls, and runtime failure modes. Fintech teams often underestimate that overhead during strategy discussions and discover it later during incidents, audits, or release freezes. If your platform maturity is low, moving too early can leave you with slower delivery and higher operational strain than the monolith you were trying to escape.
The practical answer is disciplined selectivity. You do not modernize a fintech stack by declaring victory over the monolith. You modernize it by removing the friction points that limit growth, release quality, resilience, and regulatory control. That may lead to microservices, a modular monolith, event-driven components, or a mix of all three. Your job as a technology leader is to choose the form that improves outcomes, not the form that sounds modern in a board update.
When Do Microservices Solve Real Problems Instead Of Creating Them?
Microservices solve real problems when you are dealing with organizational scale, release coordination pain, uneven workload patterns, and fault isolation requirements that a monolith can no longer handle cleanly. They are most useful when separate teams own separate business capabilities and need to ship changes without waiting for a central deployment train. In fintech, this tends to show up when customer onboarding, payments processing, pricing logic, notifications, document services, dispute handling, and external partner connectivity all need to move at different speeds under different risk controls.
You can spot the tipping point in daily delivery friction. If a small update to communication preferences requires regression testing against payment execution, or if a new identity verification rule risks destabilizing unrelated account features, your system boundaries are no longer serving the business. You are paying the price of shared code paths, shared release windows, and broad blast radius. Microservices can reduce that pain when you cut them along business capability lines and give teams true ownership of code, runtime, and data.
The strongest reason to adopt microservices is not technical fashion. It is the need for independent change. A payments team should not wait on the customer portal team to release a fix. A fraud team should not share deployment risk with statement generation. A partner integration service should be able to scale for traffic spikes without dragging the whole core stack with it. When those needs are frequent and measurable, decomposition becomes a business lever rather than a design experiment.
You should also tie the decision to delivery and recovery metrics. Look at deployment frequency, lead time for changes, change failure rate, and mean time to restore service. If you cannot show that the architecture is blocking progress on those measures, the case for microservices is still weak. Fintech modernization needs a scorecard tied to execution, not just architecture diagrams and platform slogans.
Microservices create problems when teams split too early, cut services by technical layer instead of business domain, or keep central dependencies that erase service autonomy. Shared databases, synchronous chains across half the estate, and weak observability can turn a neat service map into a distributed monolith. You then inherit network latency, partial failures, tougher debugging, and no real gain in delivery speed. That is why experienced architects push for restraint. Microservices pay off when your operating model is ready for them and your service boundaries are earned, not guessed.
What Is The Safest Way To Migrate A Legacy Fintech Monolith Without A Risky Rewrite?
The safest path is incremental extraction using the strangler fig pattern. You keep the monolith running, place a routing or application programming interface layer in front of it, and move one capability at a time into a separate service. That lets you retire old functionality gradually instead of betting the company on a full replacement program. In fintech, that is usually the only responsible route because the system still has to process transactions, support compliance controls, and handle production traffic during the migration.
A big-bang rewrite looks clean on a whiteboard and brutal in real delivery conditions. It forces teams to rebuild old logic, reinterpret years of business rules, revalidate hidden edge cases, and freeze large portions of the roadmap while the new estate catches up. That creates execution risk, budget strain, and leadership fatigue. A staged migration contains those risks by limiting the blast radius of every architectural move.
You should start by finding stable seams in the existing platform. Good seams include capabilities with clear inputs and outputs, limited dependence on core transaction integrity, and visible business value. Notifications, document generation, account alerts, customer communication preferences, pricing calculators, and partner connectors often fit this profile. These are useful extraction targets because they deliver practical gains without forcing immediate surgery on the most sensitive transactional paths.
An anti-corruption layer matters during the transition. Legacy systems often carry data models, naming conventions, and business assumptions that do not belong in your target architecture. If you let every new service talk directly to the monolith on legacy terms, you export old problems into the new stack. A translation boundary preserves clean contracts, limits leakage from old models, and gives you more freedom to refine service interfaces over time.
You should also decide what success looks like before you extract anything. Reduced release coordination, shorter lead times, lower mainframe or core-system load, fewer production incidents tied to a given capability, and improved observability are strong modernization signals. If you cannot measure value after the first few extractions, pause the program and fix the underlying operating issues. Incremental migration works only when each move leaves the estate better than it was before.
How Do You Split A Monolith Into Microservices Without Creating A Distributed Monolith?
You split a monolith safely by starting with business domains, not technical layers. Services should map to capabilities your company can name, fund, own, measure, and change independently. Customer onboarding, transaction monitoring, statement delivery, merchant settlement, loan servicing, partner onboarding, and communication preferences are business capabilities. User service, database service, or common logic service are usually signs that the cut is too generic and the coupling will return through the side door.
Domain-Driven Design helps because it forces you to define bounded contexts before you define service boundaries. A bounded context is a business area with its own terms, rules, workflows, and ownership. That discipline prevents the common fintech mistake of splitting the codebase into dozens of services that still share the same language, the same data assumptions, and the same operational dependency chain. If your services cannot change independently, they are not separate in any meaningful way.
Data ownership is where many decompositions fail. Each microservice needs clear control over its own domain data. The moment multiple services write freely into one shared database, your service boundary becomes cosmetic. Teams cannot evolve schemas independently, failures become harder to isolate, and transaction behavior remains tangled across domains. Fintech firms are often tempted to share databases during the transition to save time. That shortcut tends to delay the pain, not remove it.
You also need to police synchronous dependencies. A service that cannot complete useful work unless three or four downstream services respond in sequence is fragile by design. You then get latency amplification, cascading failures, and hard-to-explain production behavior. Event-driven integration, local data copies for read needs, and carefully designed contracts are often better choices for non-immediate interactions. You preserve autonomy and reduce the chance that one degraded component drags down the rest of the chain.
Choose early services with the cleanest ownership boundaries. In most fintech estates, the best first candidates are peripheral but important capabilities, not ledger-critical processing. Communication engines, statement generation, document workflows, pricing engines, sanctions screening adapters, and external integration gateways are easier places to prove that the team can own a service end to end. If you rush straight into the most tightly coupled transactional core, you raise the chance of recreating old dependencies across network calls instead of internal function calls.
Avoid service count vanity. More services do not mean more maturity. Many failed migrations begin with an executive target for a certain number of microservices and end with brittle systems that nobody can support gracefully. Your goal is fewer coordination points, cleaner ownership, and better runtime behavior. If that requires ten services instead of fifty, ten is the better architecture.
How Do Fintech Teams Handle Data Consistency, Compliance, And Security In Microservices?
Fintech teams handle data consistency by accepting that distributed systems replace simple all-in-one transactions with explicit consistency design. You need to decide which workflows require immediate transactional control and which can tolerate delayed synchronization. Ledger posting, balance integrity, and funds movement usually demand tight correctness guarantees. Customer alerts, reporting views, promotional eligibility flags, and some back-office workflows can often run on asynchronous patterns if the controls are clear and the audit trail is strong.
Database-per-service is a core design rule because it protects ownership and change independence. That does not mean every service needs a completely different technology stack. It means each service owns its write path, schema decisions, and lifecycle. Other services access that data through contracts, events, or approved interfaces rather than direct database joins. This is how you prevent hidden coupling from undermining the architecture you are trying to build.
Eventual consistency becomes part of normal system design in a microservices estate. You need idempotency, retries, dead-letter handling, compensating actions, and clear state transition logic. Your teams also need discipline around reconciliation. In fintech, delayed consistency is acceptable only when the business process has controls for correction, visibility, and dispute handling. If a process cannot tolerate even short-lived divergence, keep it local to one service boundary or maintain it in the monolith until you can redesign it safely.
Compliance pressure rises with service count because the number of assets, interfaces, and change points rises with it. You need stronger audit logging, immutable event history where appropriate, access control tied to service identity, encryption in transit and at rest, and policy enforcement integrated into deployment pipelines. Manual checks do not scale in a distributed estate. You need guardrails built into the platform so that teams inherit safe defaults instead of rebuilding controls service by service.
Security architecture also changes shape. In a monolith, teams often rely on a hard perimeter and shared trust assumptions inside the environment. In microservices, internal traffic becomes part of your threat model. Service identity, mutual transport layer security, secrets management, network segmentation, role-based access control, and policy-as-code become standard operating requirements. If these controls are weak, your architecture may gain modularity while losing confidence during audits and incidents.
Resilience is part of governance, not a separate technical afterthought. You need timeouts, circuit breakers, bulkheads, fallback logic, replayable events, and tested disaster recovery procedures. A distributed fintech platform must tolerate partial failure without corrupting business state or losing traceability. That means your service design, operational playbooks, and controls all need to work together. Architecture, risk, and operations stop being separate disciplines when your system depends on independent services communicating under load.
What Operating Model, Platform, And Observability Do You Need Before Migration?
You need an operating model that supports service ownership, independent deployment, and rapid issue diagnosis before you scale out microservices. If your teams still hand changes across multiple groups for build, release, access approval, and production support, decomposition will multiply friction instead of removing it. A service architecture demands accountable teams that can own code, runtime, metrics, incidents, and improvement work without waiting on a long chain of central approvals.
Your platform also needs standardization. Teams need a consistent path for provisioning environments, managing secrets, enforcing policies, registering services, routing traffic, capturing logs, collecting metrics, and tracing requests. Without these defaults, every service team invents its own runtime model. That creates security drift, uneven reliability, and support problems that become visible only during outages or audits. A strong platform team does not replace service ownership. It enables it with shared standards and paved roads.
Continuous Integration and Continuous Delivery must be real, not aspirational. You need automated testing at the right levels, dependable build pipelines, deployment automation, rollback procedures, and release controls appropriate for regulated workflows. If releases are still fragile in the monolith, microservices will not fix that weakness. They will distribute it across more units and make production coordination harder.
Observability is one of the clearest readiness tests. You should be able to trace a request across system boundaries, correlate logs with metrics, identify dependency failures quickly, and understand service health without assembling a war room every time something breaks. Distributed tracing, centralized logging, service-level dashboards, structured events, and clear alerting thresholds are not optional extras. They are basic operating requirements for a fintech service estate.
You also need governance that moves at delivery speed. Architecture review cannot become a bottleneck that blocks every change, yet standards still need teeth. The answer is a thin but strict operating model: approved patterns, reusable templates, contract governance, reliability standards, security policies in pipelines, and measured exceptions. This keeps teams moving without letting the estate drift into chaos.
Readiness should be visible in metrics. Frequent deployments, stable recovery times, low change failure rates, and clear service ownership are signs that your organization can handle distributed systems. If incidents regularly turn into long forensic exercises, if environment parity is poor, or if nobody can answer who owns a service in production, your microservices program is ahead of your operating maturity. Fix that gap before you add more moving parts.
What Does A Realistic Fintech Modernization Roadmap Look Like For The First 12 Months?
Your first year should focus on creating control, proving value, and avoiding premature scale. The opening phase is diagnosis. You need an architecture inventory, dependency mapping, service candidate identification, production pain analysis, and a clear view of which parts of the monolith change most often and fail most expensively. That gives you a modernization backlog based on business drag rather than internal opinion.
During the early months, define your target operating rules. Set standards for service boundaries, application programming interfaces, event contracts, observability, deployment pipelines, identity, secrets, and data ownership. Establish the platform capabilities teams will use by default. This work is less glamorous than announcing a microservices program, yet it is what determines whether your migration becomes orderly or chaotic. If you skip it, every later service extraction gets slower and riskier.
Your first extraction should be small enough to control and important enough to matter. Notifications are often a strong candidate because they touch customer experience, generate release friction, and can often be separated from the transaction core. Partner integration adapters, statement generation, or document services can also work well. Pick one area where you can reduce coupling, improve deployment independence, and show cleaner observability within a short cycle.
Midyear, your focus should shift from architecture planning to proof through production outcomes. Can the extracted service deploy on its own? Does it reduce release contention in the monolith? Can the team detect and resolve incidents faster? Has core-system load fallen in a measurable way? These are the questions that validate the program. Without measured gains, a modernization roadmap is just a sequence of technical tasks.
By the later part of the first year, you should have one or two services in production, a functioning migration seam, a stronger platform baseline, and better understanding of which domains deserve extraction next. You should also know where not to force decomposition yet. Some tightly coupled flows belong in a modular monolith longer than executives may prefer. Resisting bad cuts is part of good leadership.
A realistic roadmap does not promise a finished microservices estate in twelve months. It delivers stronger architecture discipline, lower-risk extractions, clearer ownership, and improved delivery metrics. If those gains are visible, you have earned the right to expand. If they are not, hold the line, fix the weak points, and keep the estate coherent. Speed matters in fintech, but controllable speed matters more.
What Mistakes Push Fintech Modernization Off Track?
The biggest mistake is treating microservices as the strategy instead of a tool inside the strategy. When leaders announce a target architecture before diagnosing delivery pain, service boundaries, and platform readiness, teams start optimizing for conformance rather than business outcomes. That often leads to too many services, rushed decomposition, and weak contracts. The system becomes harder to understand long before it becomes easier to change.
Another common mistake is splitting by technology ownership instead of business ownership. Infrastructure teams may end up driving the decomposition because they control the platform, yet they do not own the business workflows that need autonomy. Product-aligned teams need to shape service boundaries. If the architecture ignores how the business actually changes, services will look neat in diagrams and fail under real release pressure.
Shared data is another repeat offender. Teams often promise they will separate the database later, after the service is up and running. Later rarely arrives. The temporary shortcut becomes a permanent dependency, and the new service remains entangled with the monolith. Every schema change becomes negotiation, every production issue gets harder to isolate, and the architecture pays the cost of distribution without earning the benefit of autonomy.
Weak observability and immature support models also derail migrations. Teams create services faster than they create support discipline. Logs are inconsistent, alerts are noisy, traces are missing, and on-call ownership is unclear. When incidents hit, engineers spend more time discovering system behavior than fixing it. That is expensive in any sector. In fintech, it also damages confidence in the modernization program itself.
A quieter but damaging mistake is underestimating the human side of ownership. Microservices require teams to think in terms of product capability, operational responsibility, and service lifecycle management. Engineers need support, standards, and a path to grow into that model. If the organization keeps old handoff habits while introducing new architecture, it creates confusion on top of complexity. The system changes, but the delivery behavior does not.
How Should You Measure Whether Modernization Is Working?
You should measure modernization through delivery, resilience, and operational clarity. Track deployment frequency, lead time for changes, change failure rate, and mean time to restore service. These metrics tell you whether the architecture is helping teams ship safely and recover quickly. If your service count rises while these indicators stay flat or get worse, the program is missing its target.
You should also measure coupling reduction. Look at how many releases still require coordination across unrelated domains, how many incidents cross service boundaries, and how much test scope is needed for a typical change. A strong modernization program reduces unnecessary coordination. Teams should need fewer broad regression exercises and fewer cross-functional approvals for changes that belong to one business capability.
Operational visibility is another useful signal. Can the owner of a service explain its dependencies, health indicators, failure modes, and recovery procedures? Can production teams trace a customer-impacting request from entry point to outcome? Can audit and risk teams get the records they need without detective work across five platforms? If the answer improves over time, the architecture is becoming easier to govern, not just more distributed.
Business impact matters too. You should connect modernization to cycle time on key initiatives, speed of compliance-related changes, reduction in core-system bottlenecks, and support for new product launches. Fintech modernization should help you release new capabilities faster, integrate partners more cleanly, and contain failure to smaller domains. If those gains are not visible, then the architecture may be consuming energy without returning value.
One more measure deserves attention: restraint. A healthy program says no to extra services when the case is weak. It pauses when platform capabilities are behind demand. It consolidates when a service split proves artificial. Measuring success includes measuring how often your teams make disciplined non-decisions. Mature architecture leadership is visible not just in what gets built, but in what gets avoided.
What Is The Best Way To Modernize A Fintech Monolith?
- Start with a modular monolith or selective service extraction.
- Use the strangler fig pattern, not a full rewrite.
- Cut services by business domain and owned data.
- Measure delivery speed, resilience, and auditability.
Build The Estate You Can Run, Not The Diagram You Can Present
Your best modernization decision is the one that improves delivery, resilience, and control without outrunning your team’s ability to operate the result. If your monolith still serves the business, strengthen its modularity and remove the worst bottlenecks before you split it apart. If your domains, teams, and release pressures justify microservices, extract them one capability at a time, protect data ownership, and invest in platform standards before service count expands. The strongest fintech architectures are usually the most disciplined, not the most fashionable. If you stay focused on measurable business outcomes, your modernization program can reduce risk, speed up delivery, and leave you with an estate your teams can actually run with confidence.